Crowlin / How it works
How Crowlin works inside.
For IT and security teams: the journey of one question, connections to business systems, digital employees and the technical security of operations.
The journey of one question. Entirely inside.
Who is asking
Sign-in with a company account (Google Workspace; Microsoft 365 connected during rollout). Without a verified identity Crowlin answers nothing at all.
No identity: rejected, not “anonymous mode”What they may see
Roles, teams, projects and confidentiality level are loaded from the permission database — never from the question. Whatever is not explicitly allowed is denied.
An explicit deny always beats a roleSearching the documents
Only documents the person can access are searched — contracts, policies, documentation and other connected sources. A second, specialised model ranks the most relevant passages.
The permission filter runs on the server, not in the appA model on your hardware
The answer from your documents is written by a language model running on a GPU inside the server. Documents are never sent to OpenAI, Google or any other third-party AI service.
Company documents never go to third-party AIAn answer with citations
Every claim links to a source you can open and check. If the answer isn’t in the documents, Crowlin says so instead of making it up.
“It’s not in the documents” is a valid answerAudit record
Who asked, what they were allowed to see and which documents the answer came from. Every question leaves a traceable record.
Audit trail for every questionIt knows what you know. And in the morning, what changed yesterday.
Crowlin connects to the sources where your knowledge already lives. Nothing to rewrite, nothing to migrate. Sync runs overnight and every document carries its own permissions.
Documents, wikis and project tools
Contracts, policies, data sheets, ISO documentation, meeting notes. Today: uploaded files (PDF, Word, Excel, CSV) plus Confluence and Jira connectors; SharePoint and network drives are connected during rollout. Spaces and folders map to confidentiality levels.
ERP and other business systems
Orders, jobs, stock, invoices, complaints. We build the API connection to the system you use — SAP, Microsoft Dynamics, local ERPs or your own solution — as part of implementation.
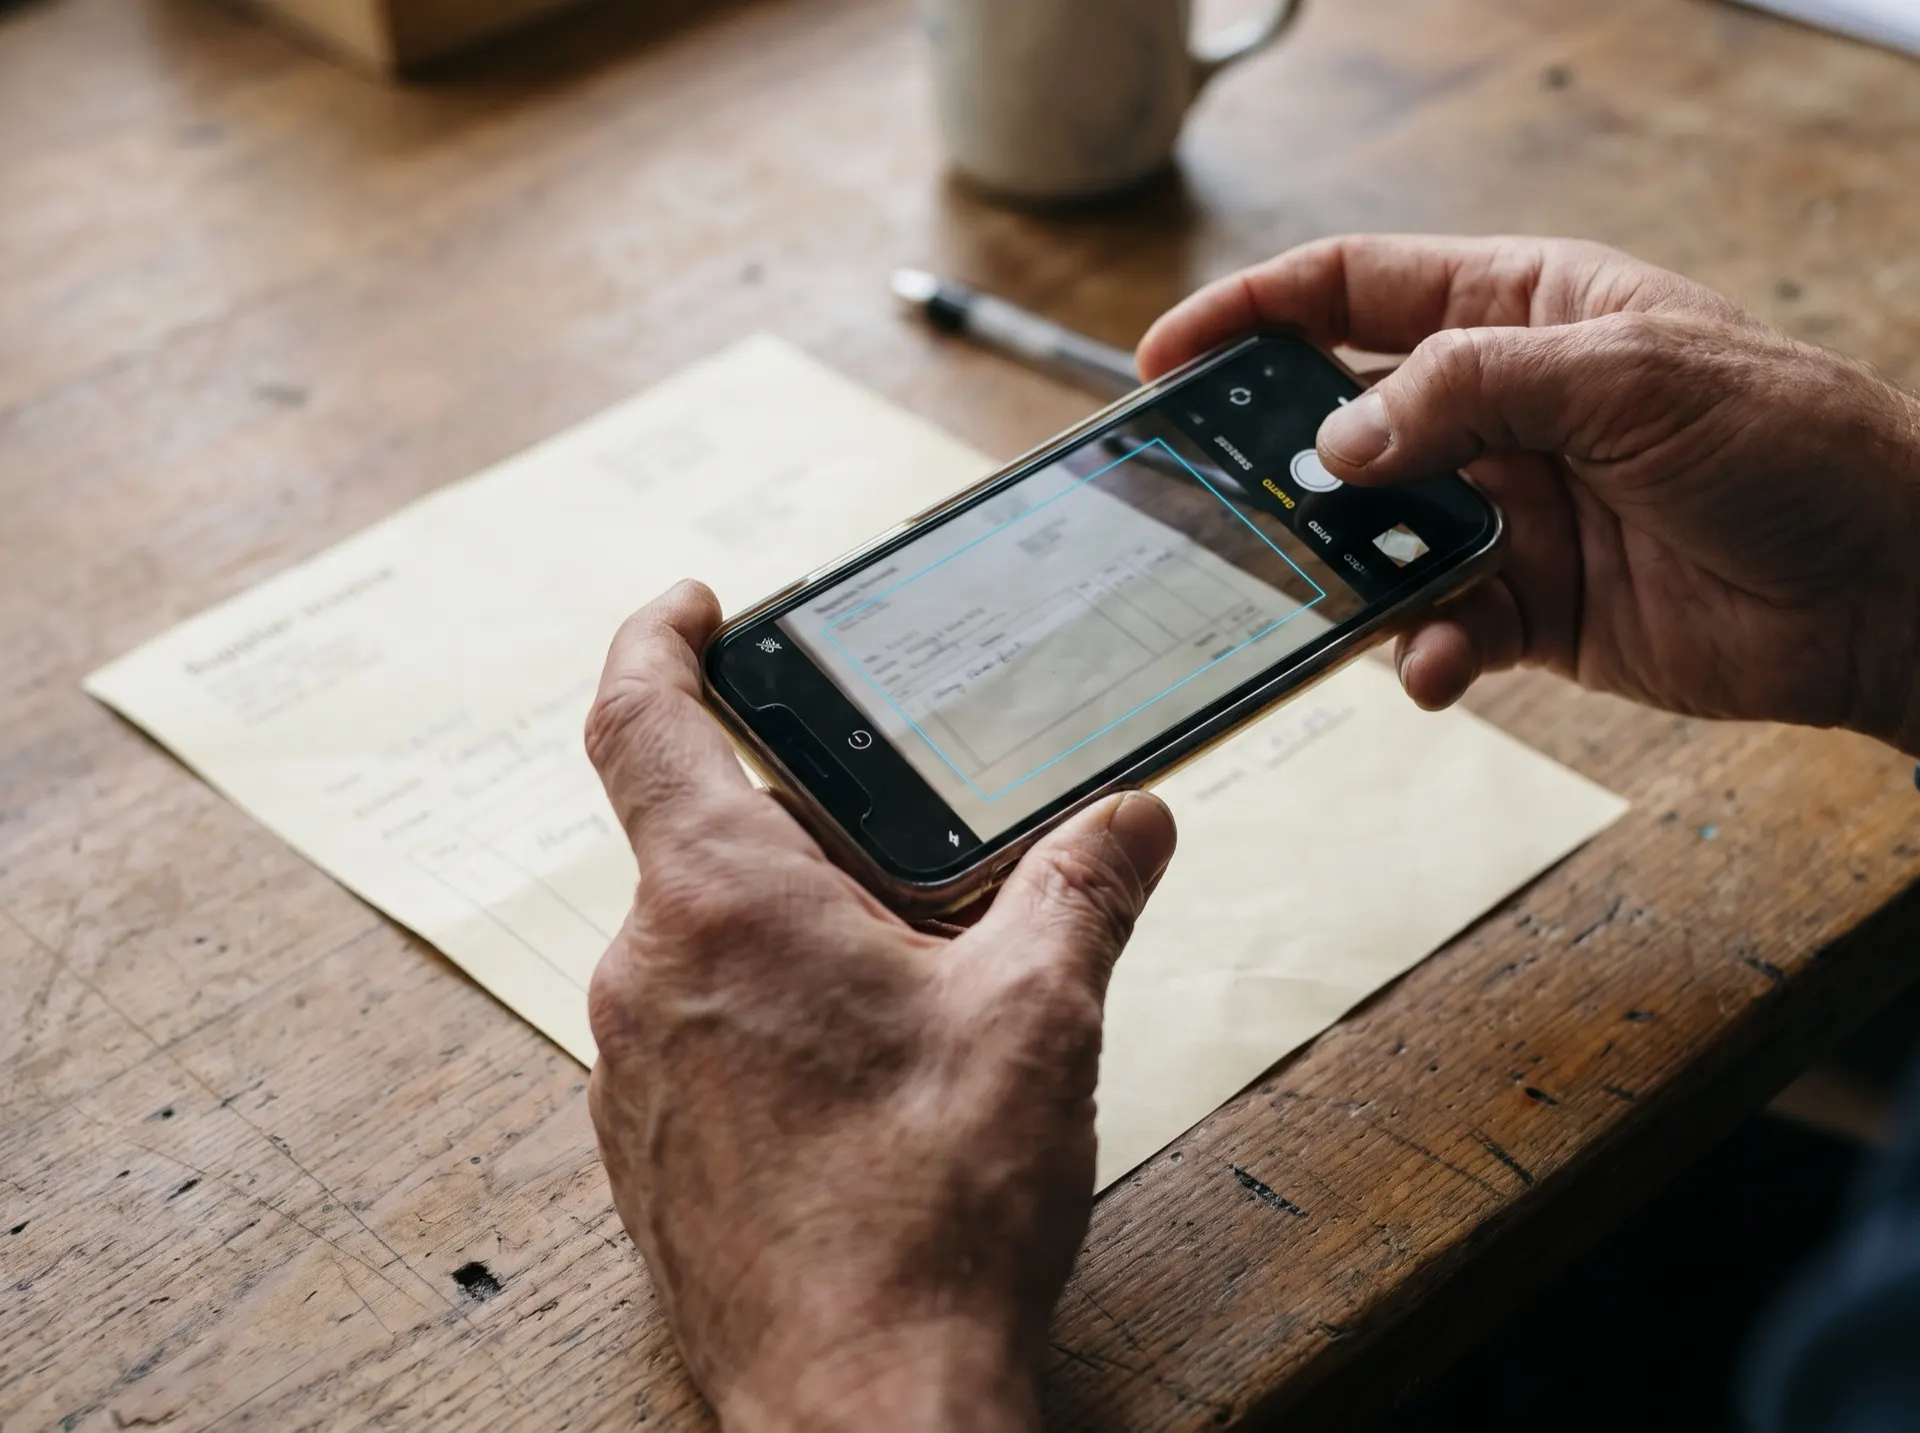
Photo of a document
Snap an invoice, delivery note or label. The text is read by the model on the server — the photo never leaves.
The server does the maths
Revenue, margins, downtime, cost of complaints. For connected systems the calculation runs directly on the data — the model doesn’t estimate numbers, it only explains them.
The web, when needed
Up-to-date information from the internet through a search engine running on the server. Only the search query goes out, never your documents. The feature can be switched off.
Digital employees with precisely defined authority.
Crowlin doesn’t just answer. Digital employees prepare a digest, assess a public tender or check documents on their own. You decide what they may do alone and what needs human approval — and which model they run on: local, or a cloud model where the data allows. Below are examples we set up around your processes.
On their own
Read, search, summarise, draft. No human intervention.
With approval
Reply to a customer, change an order status, write to the ERP. A person confirms with one click.
Humans only
Payments, contracts, deleting data. The agent prepares the groundwork, a person always decides.
Every tool has a risk class. An agent never gets a tool without an assigned class — and every action it takes is audited under the name of whoever approved it.
Morning operations digest
Goes through shift reports, orders and complaints from the last 24 hours and sends management a summary of what’s on fire.
Bid or no bid?
Extracts the requirements from the tender documents, compares them with your references and gives a reasoned recommendation.
Does the invoice match the order?
Compares every incoming invoice with the order and contract and flags differences in price, quantity or payment terms.
Draft reply to a customer
Uses data sheets, contracts and order history to draft a reply to a customer enquiry.
Security proven by tests, not promises.
Every access rule has an automated test. If any check fails or the permission database is unavailable, Crowlin would rather not answer — it never returns unfiltered data.
Data in the EU or on your premises
A server in a German data centre, a dedicated machine, or — individually — your own server room.
Encrypted backups
Daily encrypted off-server backups. We test restores regularly instead of assuming they work.
24/7 monitoring
Availability checks from outside and inside, with alerts before you notice an outage.
Every question traceable
Who, when, what they were allowed to see and which sources the model used. For audit, compliance and debugging.
We measure accuracy on your data
Every answer carries a link to its source, so it can be checked. Citations make answers verifiable but don’t make them infallible — so in a pilot we build a control set of questions from your company with correct answers and measure accuracy against it. Where the answer isn’t in the documents, Crowlin says so.
Infrastructure and operations
- All services in an isolated internal network; only HTTPS is exposed
- Server access by SSH key only, no passwords; protection against repeated login attempts
- Default-deny firewall and automatic security updates
- Encrypted connections (TLS) and company sign-in enforced at the gateway
- Daily encrypted backups of the database and vector index, off-server copies, regular restore tests
- Server and GPU monitoring, external uptime checks and tracing of every model request
Technical FAQ
Is this ChatGPT with a different logo?
Which model does Crowlin use?
Is a self-hosted model as smart as the biggest ones?
How are other systems connected?
Can our own applications use Crowlin?
We’ll show you on your own data.
We’ll show you Crowlin on a sample of your documents in an isolated space. We delete the data after the demo on request.